
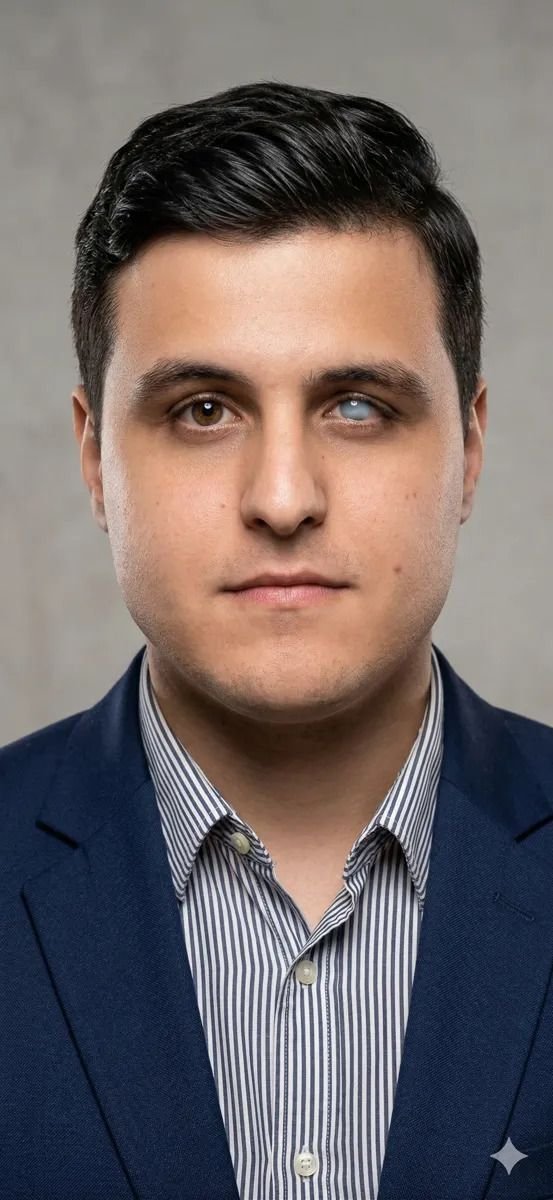
How BNVD makes vulnerability intelligence accessible in Portuguese
Juan Mathews Rebello Santos founded bnvd, Brazil’s national cybersecurity vulnerability database, which synchronizes U.S. vulnerability data and provides CVE descriptions in Portuguese. The conversation explores how AI supports development and research, why people must verify security-critical work, and how accessible information can help more people engage with cybersecurity.
Use AI to speed up development, research, and repetitive work, but keep human expertise and accountability in security-critical decisions. For discovery, build useful resources and clear technical content, and make them accessible to people and search tools.
What’s the quick origin story of your business, and what makes what you do genuinely different from the other options your customers are looking at?
I founded the Brazilian National Vulnerability Database (BNVD) to address a simple but important problem: cybersecurity information should be accessible to everyone, including professionals and organizations that do not have easy access to technical resources in Portuguese. BNVD was created to make vulnerability intelligence more accessible to the Brazilian cybersecurity community. The platform synchronizes data from the U.S. National Vulnerability Database (NVD) and provides Portuguese translations of CVE descriptions, helping security professionals, developers, students, and organizations understand vulnerabilities without having to rely entirely on English-language resources. What makes BNVD different is its focus on accessibility, localization, and democratizing cybersecurity knowledge. Beyond building a vulnerability database, I want to reduce the barriers that prevent people from entering and growing in this field. As a completely blind cybersecurity professional, Microsoft MVP, and vulnerability researcher, I also bring a perspective that is often missing from technology development: security solutions should be effective, but they should also be accessible. BNVD reflects that philosophy by making important security information easier to discover and understand for a broader audience.
Where does most of your new business come from today, and where do you wish it came from?
Today, most of the opportunities connected to my work come from my professional reputation, technical contributions, cybersecurity publications, open-source projects, and participation in the broader security community. Sharing knowledge, researching vulnerabilities, and building practical tools have helped me establish credibility and connect with people who care about cybersecurity. Through BNVD, I want to expand that reach and build stronger relationships with cybersecurity companies, educational institutions, independent researchers, and organizations that need accessible vulnerability intelligence. Over the next year, I would like more opportunities to come through strategic partnerships, organic search, technical communities, and AI-powered discovery tools. My goal is not simply to attract more visitors, but to reach people and organizations that can benefit from BNVD, contribute to its development, and help make cybersecurity knowledge more accessible in Brazil.
What’s one thing you’ve actually handed over to AI in the last year, and one thing you tried it on and went back to doing the human way?
One area where I have incorporated AI into my workflow is software development and technical research. AI tools help me explore implementation approaches, generate and review code, investigate technical problems, and accelerate repetitive tasks. As a developer who is completely blind and relies on screen readers, I am particularly interested in how AI can improve accessibility and make complex technical workflows more manageable. However, I do not treat AI-generated output as trustworthy by default. In cybersecurity, a plausible answer can still be technically wrong or introduce a vulnerability. I always need to validate results, test implementations, and apply my own technical judgment. One area I would never hand over entirely to AI is the final assessment of a security vulnerability or a security-critical decision. AI can help analyze evidence and identify possible explanations, but determining whether a finding is valid, understanding its real-world impact, and deciding how to address it require human verification and accountability. For me, the best approach is to use AI to accelerate the work, not to replace the expertise and responsibility behind it.
Have you noticed a change in how customers find you or what they already know before they reach out? Is anyone arriving through AI assistants like ChatGPT yet?
Discovery is changing as more people use AI assistants and conversational search tools to research cybersecurity topics, identify experts, and find technical resources before contacting someone directly. My work has a strong digital footprint through BNVD, open-source repositories, technical publications, professional interviews, and vulnerability research. This creates multiple ways for people to discover my work and understand my expertise before reaching out. AI assistants could be particularly valuable for a project like BNVD because they can help people find and understand vulnerability information in their preferred language. Making reliable, well-structured cybersecurity information available online is therefore increasingly important. I see AI-powered discovery as an opportunity, although I do not yet have reliable attribution data to quantify how many visitors or professional opportunities specifically originate from ChatGPT or other AI assistants. My priority is to keep building useful resources, publishing credible technical content, and making BNVD easier for both people and search technologies to discover.
If you were advising someone in your industry on all of this for the next 12 months, what would you tell them to actually do, and what would you tell them to ignore?
My advice would be to focus on building something genuinely useful, establishing credibility, and using AI to improve execution rather than chasing every new trend. First, invest in high-quality technical content and practical projects that solve real problems. In cybersecurity, trust comes from demonstrable expertise, responsible research, and solutions that people can actually use. Second, make your work discoverable. Maintain a professional website, publish clear technical documentation, contribute to open-source projects, and structure your content so that both traditional search engines and AI assistants can understand it. Third, integrate AI where it creates measurable value, such as development assistance, documentation, research support, and repetitive workflows. At the same time, maintain human oversight of security-critical decisions and verify AI-generated results. Finally, treat accessibility as a core design principle, not an afterthought. Technology should enable more people to participate, including professionals with disabilities who are frequently overlooked when products and workflows are designed. What would I ignore? The pressure to adopt every new AI tool, promises of effortless growth, and vanity metrics that do not translate into real value. Over the next 12 months, I believe the strongest results will come from combining technical depth, responsible AI adoption, accessibility, and consistent execution.
Thank you to Juan Mathews Rebello Santos and the team at bnvd for sharing what actually worked with Leaders Perception readers.
Want to share your playbook?
Leaders Perception publishes founder and operator interviews every week. A few questions, about five minutes, no calls. It is free and everyone we accept gets published.